
nFOX launches platform & open-sources Blockhouse sandbox
Tue, 27th Oct 2026 (Today)
nFOX has launched the nFOX Platform and will open-source its Blockhouse sandbox for AI workloads. Blockhouse is in beta for qualified enterprise evaluations.
The New York startup is targeting companies that want to deploy open AI models on infrastructure they control rather than rely on externally managed systems. The platform is designed to let customers evaluate, deploy and monitor those models across cloud virtual machines, rented GPU hosts and on-premises Linux servers with NVIDIA GPUs.
Alongside the platform launch, nFOX plans to release Blockhouse as open source. It describes the product as a kernel-enforced sandbox that places model runtimes in a restricted environment and limits access by default.
The software enforces boundaries below the application layer. According to nFOX, attempts by workloads to operate outside approved limits are blocked, halted and recorded, while communications are routed through a kernel-policed and audited channel called Porthole.
Runtime credentials and audit controls remain outside the model process, nFOX said. It added that approved model files are sealed with SHA-256 hashes before serving, and integrity checks can halt serving if those files are changed.
Blockhouse supports vLLM, SGLang and llama.cpp, according to nFOX. Each run records sandbox health and approved access, and Blockhouse can also report when a host cannot provide the expected protections.
Control and oversight
The nFOX Platform adds a management layer for enterprise users running multiple models across their own GPU infrastructure. Teams can choose supported serving engines and quantisation modes while using a single console to handle model approval, deployment and monitoring.
The workflow includes checks on model configuration, tokenizer settings and code-execution flags, as well as file integrity verification and testing with adversarial prompts. Once approved, models can be deployed inside Blockhouse and exposed through OpenAI-compatible API endpoints for production use.
Monitoring tools in the platform track requests, integrity checks and containment events. Runtime evidence can be fed into existing endpoint detection and response, and security information and event management workflows, with records written in canonical JSON and Parquet formats.
The system is designed to keep prompts, vectors, tokens, tool calls and audit paths within an enterprise-controlled deployment environment. That reflects growing business interest in running AI systems within internal security and compliance boundaries.
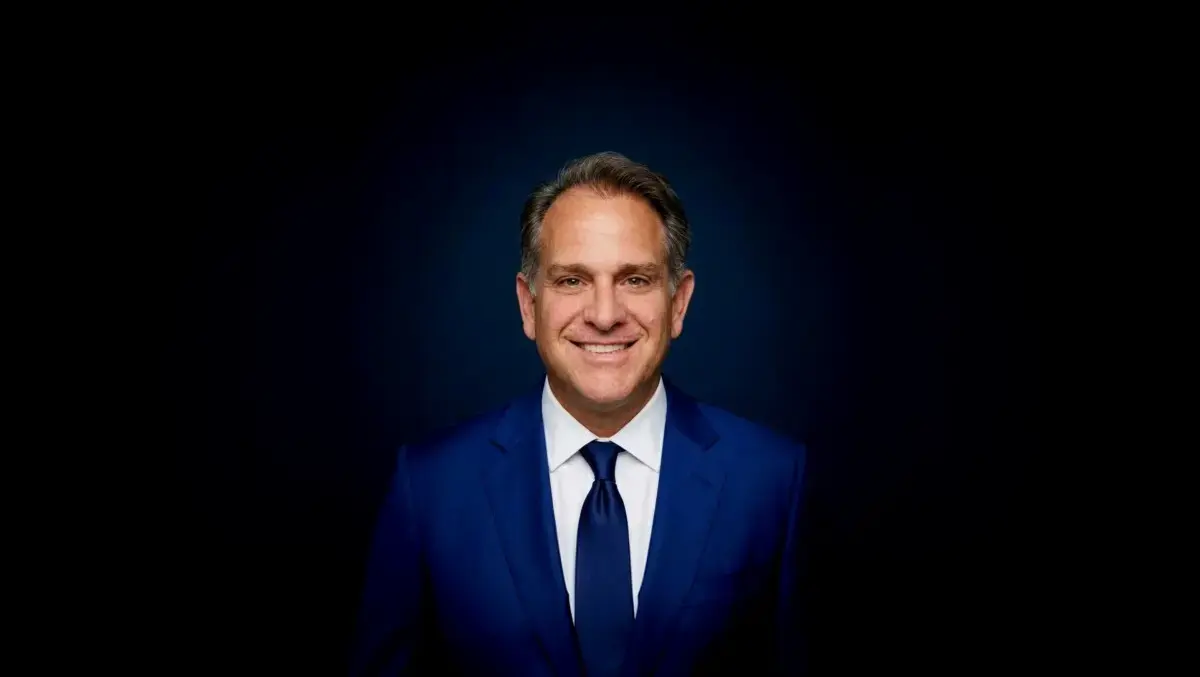
"Companies need a practical way to run AI models without giving up control of their systems and data," said Gordon Allott, founder and chief executive officer of nFOX.
"NVIDIA's Open Shell reflects the same architectural principle behind our approach: privileges should be denied by default and granted only through explicit enterprise controls. We developed Blockhouse to put clear boundaries around what AI workloads can access and do. The nFOX Platform helps teams manage those deployments and review integrity checks and containment events, giving them the evidence they need to make informed adoption decisions," Allott said.
Open source plan
Making Blockhouse open source will allow developers and enterprise security teams to inspect the implementation and assess its containment model on infrastructure they control, nFOX said. The company is positioning Blockhouse as the workload sandbox, while the nFOX Platform serves as the central management environment for deployment and oversight.
The announcement comes as more companies experiment with open models for internal use but face pressure to demonstrate tighter operational controls. In those deployments, security teams often want evidence of what a model runtime can access, how it behaves during operation and whether file integrity has been maintained.
Chris Egloff, nFOX's chief technology officer, said those questions are central to adoption decisions.
"Security teams need to understand the boundary around an AI workload and see how it behaves during operation," Egloff said.
"Blockhouse combines enforceable access restrictions with reviewable evidence, helping teams evaluate models and investigate containment events," he added.
The nFOX Platform is available now, while Blockhouse remains in beta for qualified enterprise evaluations.